
Bank of Uganda Governor Dr Michael Atingi-Ego has warned that a major cyberattack on Uganda’s increasingly interconnected digital infrastructure could move rapidly from a technical problem to a disruption of payments, loss of public confidence and, ultimately, a threat to financial stability.
Atingi-Ego’s warning places cybersecurity at the centre of Uganda’s economic transformation, arguing that the country cannot pursue digital payments, financial inclusion, digital government and artificial intelligence without simultaneously building systems capable of surviving cyber disruption.
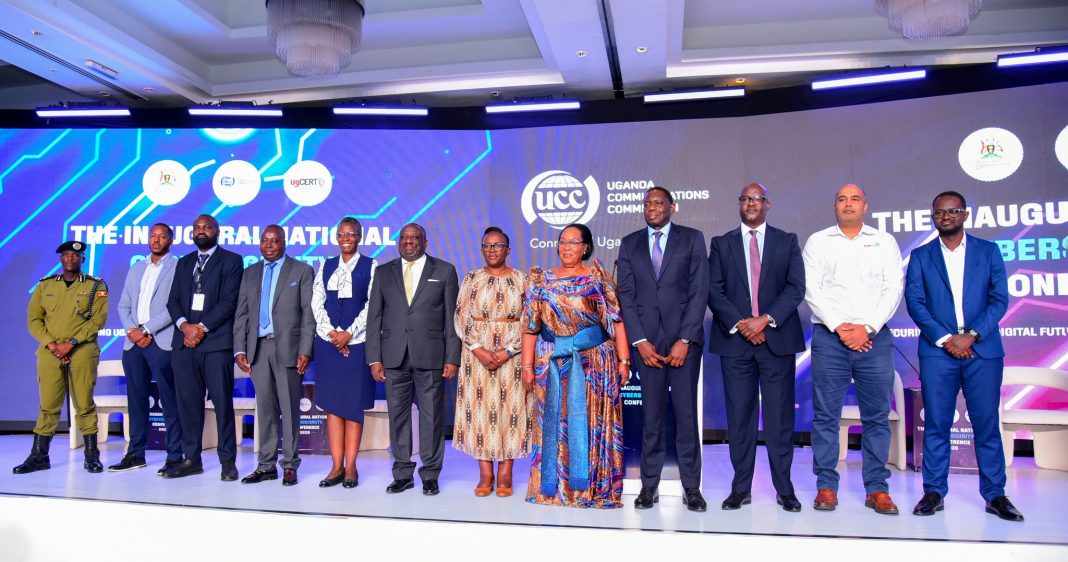
Speaking at the inaugural National Cybersecurity Conference in Kampala on August 11, Atingi-Ego said cybersecurity had moved beyond the traditional responsibility of ICT departments and become a matter for central banks, boards, chief executives, regulators and national policymakers.
“Cybersecurity is no longer the responsibility of one institution. It is a national capability,” he told a gathering that brought together regulators, security agencies, banks, telecommunications companies, technology firms, academics and development partners.
The Governor’s argument is particularly significant for Uganda’s financial sector, where banks, mobile-money operators, payment platforms and telecommunications networks are becoming increasingly dependent on one another.
He said the traditional understanding of financial stability, centred largely on capital, liquidity and balance-sheet strength, was no longer sufficient in an economy whose transactions increasingly depend on digital infrastructure.
“Financial stability has always depended on capital and liquidity; it now depends equally on the availability, integrity and reliability of the systems through which financial activity flows,” Atingi-Ego said.
A cyberattack is no longer just an IT problem
Uganda’s digital expansion has created a much larger target for cybercriminals.
Atingi-Ego said an estimated 23 million Ugandans, almost half the country’s population, are now online, using digital platforms for commerce, education, financial services and government services.
The Government’s Digital
Transformation Roadmap is seeking even wider adoption, targeting 90% broadband coverage and 90% of citizens accessing e-services online by 2040.
But the Governor cautioned that every additional digital connection also creates another potential entry point for attackers.
Uganda Police statistics cited in his speech show reported cybercrime cases rising from 245 in 2023 to 474 in 2024, an increase of more than 93%, before falling to 412 in 2025.
The number remains substantially above the 2023 level, while the financial losses associated with cybercrime run into billions of shillings annually. A NITA-U assessment cited by Atingi-Ego also found that roughly four in 10 Ugandan small and medium-sized enterprises had experienced some form of cyberattack.
The concern is not merely that individual Ugandans or companies could lose money.
It is that an attack on one part of the digital economy could spread through the connections between institutions.
“The power of digital technology comes not from individual systems but from the connections between them,” Atingi-Ego said.
A compromised telecommunications network could affect financial services. A stolen digital identity could provide access to multiple services. A failure at a common technology provider could affect several institutions simultaneously.
That interconnectedness, he argued, means Uganda must begin thinking about cybersecurity at the level of an ecosystem, rather than treating each bank, ministry, telecom operator or technology company as a separate island.
The regional lesson
Uganda is not confronting this problem alone.
Across East Africa, governments are attempting to reconcile rapid digitalisation with a threat environment that increasingly crosses national borders.
Kenya, Rwanda, Tanzania and Uganda have all developed national cybersecurity frameworks, while the East African Community is working towards greater regional cooperation on cyber and data protection. An EAC initiative has been advancing a regional Computer Emergency Response Team model intended to improve coordination when cyber incidents cross national boundaries.
This regional dimension matters because East Africa’s digital economy is increasingly interconnected through mobile money, electronic payments, telecommunications networks, fintech platforms and cross-border commerce.
An attacker does not necessarily need to remain inside Uganda’s borders to affect a Ugandan institution.
For Uganda, the lesson from its neighbours is therefore less about copying one country’s cybersecurity system than recognising the need for regional coordination, common standards and rapid information-sharing.
That is consistent with Uganda’s own National Cybersecurity Strategy 2022–2026, which calls for a secure and resilient cyberspace, stronger threat preparedness and response, protection of critical information infrastructure, public-private partnerships and regional cooperation.
Uganda has regulations. The question is implementation.
Uganda has not been starting from scratch.
The country adopted its National Cybersecurity Strategy for 2022–2026, while the Government in July launched the Updated National Information Security Framework 2026.
The new framework provides government institutions with cybersecurity assessment tools, minimum security controls and guidance intended to improve institutional resilience and protect critical information infrastructure.
For the financial sector, Bank of Uganda introduced Cyber and Technology Risk Management Guidelines in December 2024, requiring supervised financial institutions to strengthen governance, data protection and security controls.
The challenge, however, is turning regulations into operational resilience.
Atingi-Ego warned against a situation where institutions possess impressive cybersecurity policies but have never tested whether those policies work during a real crisis.
“What happens if our primary system fails?” he asked. “If our key technology provider is unavailable for a day? If several institutions are hit simultaneously?”
He said institutions must know who makes decisions, who communicates with the public, who coordinates the response and how quickly essential services can be restored.
His most pointed warning was that an untested contingency plan is not genuine resilience.
“A continuity plan nobody has rehearsed, a backup nobody has restored, is not yet a capability. It is a hope written down on paper,” he said.
Kenya, Rwanda and Tanzania offer different lessons
The regional comparison exposes an important issue for Uganda.
Kenya’s experience demonstrates the scale of the threat facing a highly digitised economy. Its large mobile-money, fintech and e-government ecosystem has created an extensive digital attack surface, making cybersecurity a matter of economic rather than merely technological security.
Rwanda, meanwhile, has placed strong emphasis on coordinated national cybersecurity institutions and the protection of its rapidly expanding digital public infrastructure.
Tanzania has similarly developed a national cybersecurity framework and institutional mechanisms for responding to cyber threats.
The broad regional trend is therefore clear: governments are moving away from seeing cybersecurity as something handled exclusively by technical specialists and towards national systems involving regulators, security agencies, telecommunications companies, banks and government.
The EAC’s move towards a regional response mechanism is particularly important because cybercrime does not stop at border posts.
For Uganda, Atingi-Ego’s argument pushes that regional debate one step further: cybersecurity must also become part of financial-stability policy.
From prevention to resilience
Atingi-Ego does not believe Uganda can build a system that prevents every cyberattack.
Instead, he wants institutions to become capable of functioning when attacks inevitably occur.
He compared cyber resilience with the way financial regulators prepare for economic shocks.
Banks do not maintain capital buffers because regulators believe financial crises are impossible. They maintain buffers precisely because shocks happen.
“Cyber resilience deserves the same rigour,” he said.
That means institutions should continuously test their systems, rehearse emergency responses, restore backups, identify weaknesses in third-party providers and establish clear lines of communication before a crisis occurs.
It also means that cybersecurity cannot be outsourced entirely to an organisation’s ICT department.
“Cybersecurity is no longer solely the responsibility of ICT departments; it is a boardroom issue, an executive leadership responsibility, and increasingly a matter of national policy,” Atingi-Ego said.
The trust problem
At the centre of Atingi-Ego’s argument is a less visible but potentially more damaging consequence of cyberattacks: loss of trust.
A citizen who fears losing money may stop using digital payments. A business that doubts the reliability of an online platform may avoid investing in it. An investor who sees repeated disruptions may demand greater risk protection or simply take capital elsewhere.
“Trust is not a soft virtue added on top of sound economics; it is infrastructure — as real, and as load-bearing, as a road or a power line,” Atingi-Ego said.
That makes cybersecurity part of Uganda’s broader development agenda.
The country wants more people online, more businesses using digital platforms and more government services delivered electronically. But the more Uganda asks its citizens and businesses to rely on digital systems, the greater the economic consequences if those systems repeatedly fail.
‘Build security in’
Atingi-Ego also rejected the argument that cybersecurity should slow technological innovation.
Instead, he said security should be incorporated into new systems from the beginning.
“Build security in; do not bolt it on,” he said.
That principle is becoming increasingly important as Uganda expands digital identity, electronic payments, artificial intelligence and online public services.
The Governor’s warning about artificial intelligence was particularly timely. He noted that the capabilities available to attackers and defenders are changing rapidly, meaning cybersecurity policies cannot remain static.
Uganda’s challenge, therefore, is not simply to produce another cybersecurity policy. It is to create institutions capable of adapting as quickly as the technology and threats evolve.
The bigger East African challenge
The comparison with Kenya, Rwanda and Tanzania ultimately points to a common problem across the region.
East Africa is building one of the continent’s most dynamic digital economies while simultaneously confronting a cyber threat landscape that is becoming more sophisticated and interconnected.
The region’s governments have made progress in creating national strategies, regulatory frameworks and cyber-response institutions. The EAC’s efforts towards regional coordination recognise that national boundaries offer little protection against digital attacks.
But Atingi-Ego’s speech highlights the next test: whether these frameworks can operate together during a real regional crisis.
For Uganda, that means strengthening cooperation between the central bank, telecom regulator, government agencies, security institutions, banks and technology companies — while also deepening cooperation with neighbouring countries.
The Governor’s proposed answer is a national compact built around collaboration, resilience and trust.
Uganda’s digital future, he said, will not be secured by technology, regulation or investment alone.
“It will be secured by institutions, systems and people choosing, deliberately and repeatedly, to work together,” he said.
The implication is stark: as Uganda becomes more digital, a cyberattack is no longer simply a problem for the IT department to fix.
It can become a problem for the bank, the telecom network, the government, the payments system, businesses and ultimately the economy.
And that is why, in Atingi-Ego’s formulation, cybersecurity has moved from the server room to the centre of Uganda’s economic policy debate.